Google introduces the Agent2Agent protocol
Google introduced Agent2Agent, an open protocol intended to help agents communicate, collaborate, and delegate work across frameworks.
By Hypler editorial team · Source: Google.
Original source date: .
Hypler publication: . Hypler updated: .
Estimated reading time: 4 minutes.
Topics: A2A, interoperability, agents

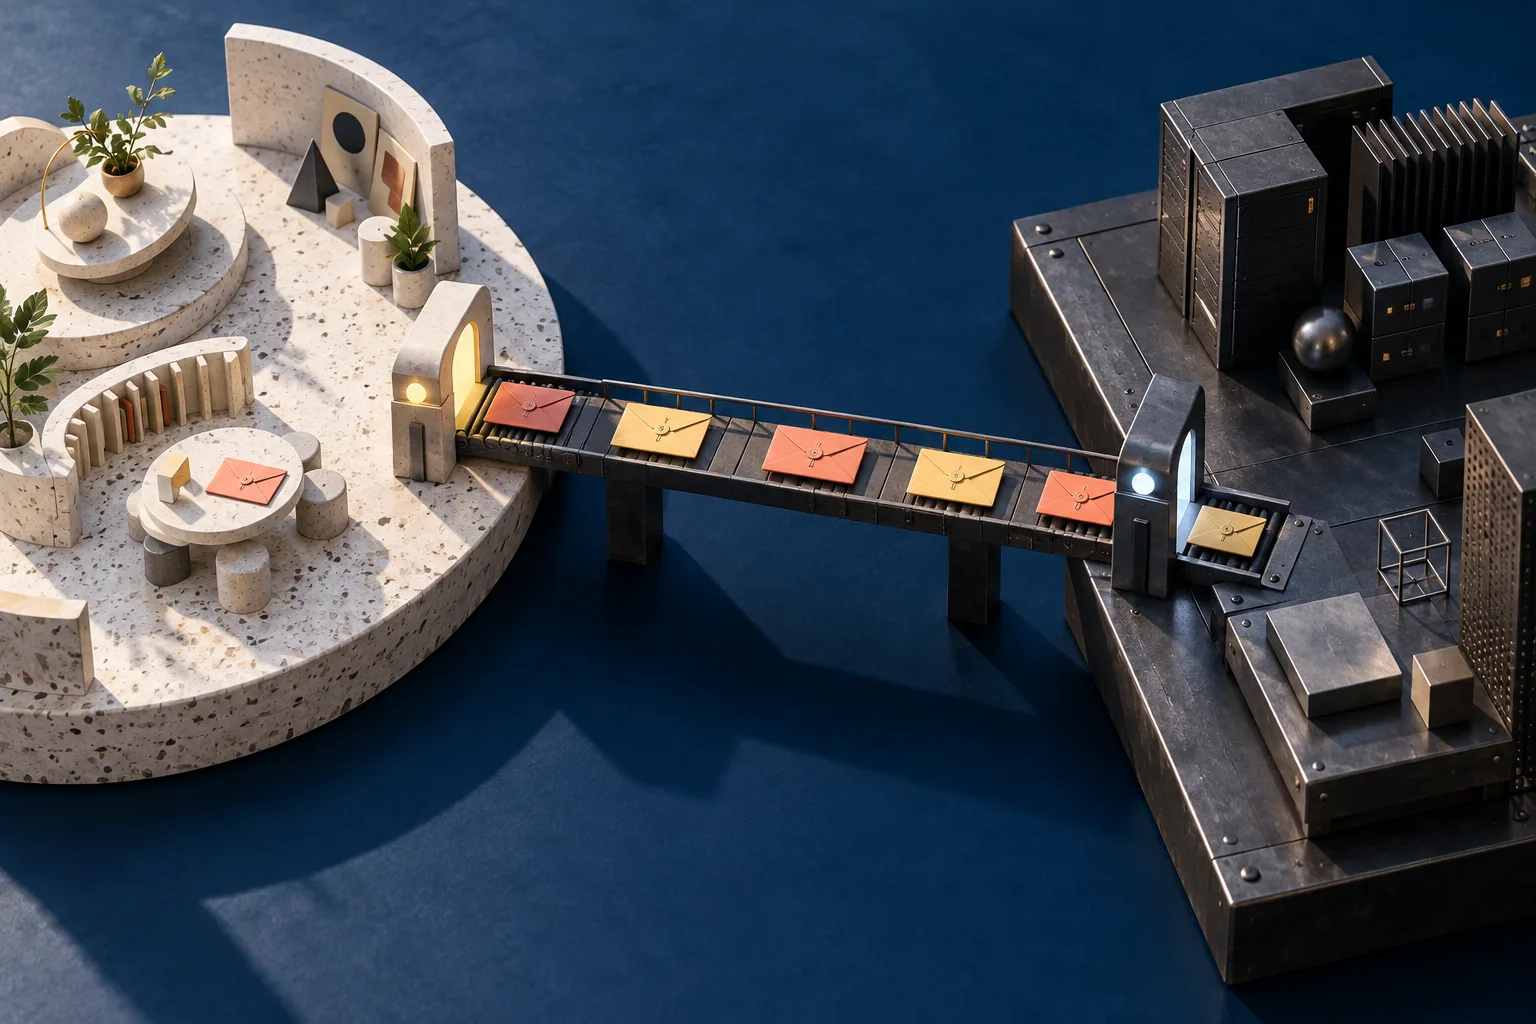
Interoperability creates a new caller
Google presented Agent2Agent as a protocol for agents to communicate, discover capabilities, and exchange work across frameworks. That addresses transport and representation. It does not decide whether a service should trust the caller, release particular data, or accept a delegated action in this transaction. A task card can advertise a capability without proving the caller may use it. This historical description makes no claim about a current protocol version, certification, production interoperability, or the security posture of any implementation.
Delegation must lose power as it travels
A delegated grant should be narrower than the caller’s own grant. It can bind an audience, task ID, capability list, classification, expiry, action or spending budget, and a revocation handle. The receiving service authenticates the caller, validates the task schema, and applies its local policy. Discovery before trust should reveal only public metadata; otherwise it becomes an inventory of sensitive operations. In Hypler’s view, an A2A-style envelope carries work between systems, while authorization and receipts remain local responsibilities.
Status language can conceal a bad outcome
Replayed messages, confused deputies, incompatible status vocabularies, duplicate callbacks, premature success reports, and grants revoked in flight all turn a simple handoff into a state-management problem. Completion should come from signed, idempotent transitions, not from a fluent textual summary. Accepted, in-progress, blocked, failed, cancelled, and completed need explicit meanings. Child tasks need their parent link and denials need a reason. A remote answer without required evidence may be informative, yet it cannot become a trigger for local execution.
A catalog request stays read-only
Hypothetical example: imagine a planning agent asking an external catalog agent to compare approved integration categories. The caller grants a read-only search scope and a fifteen-minute expiry. The recipient verifies the signature and returns candidates with source URLs; it has no budget, internal notes, or procurement credentials. Its response includes prose telling the system to enable a connector. The local orchestrator treats that prose as content rather than a transition. A human analyst selects a candidate, and a different local approval process handles onboarding. The receipt names both agents, grants, task states, sources, and the denied enable request.
Connection tests must include betrayal and drift
An implementation should test expired and revoked grants, wrong audiences, replayed task IDs, schema downgrade, unknown capability claims, duplicate callbacks, remote timeout, and embedded instructions. An external service must not convert a read grant to write access or cause a local tool call through text. Status mapping needs to preserve failure and cancellation. Key rotation, audit-log retrieval, and the provenance chain from parent task to child evidence also need proof. Passing protocol conformance remains necessary; local classification, authorization, and incident handling are separate evidence.
Trust is established in stages
An external agent deserves the same onboarding discipline as a new service. Begin with identity verification and synthetic, read-only tasks. Review task schema, error model, callback behavior, retention claims, and incident contact. Add one capability at a time and exercise revocation after each grant. A production trust tier cannot follow merely from parsing a protocol card. Policy, key rotation, telemetry, and offboarding each need an owner. Deliberately testing a version mismatch also shows whether an upgrade will fail safely instead of making an ambiguous fallback.
Hypler’s editorial judgment
Agent2Agent makes compatible messages possible. It does not remove the harder work of controlling a relationship between services. Hypler treats inter-system delegation as an exchange of bounded identity, work, status, and evidence, designed so an operator can inspect, deny, revoke, and recover the request. That standard favors a slower first connection when needed, because it leaves the relationship understandable after a failure or revocation.
Hypler analysis
Hypler’s view
Agent-to-agent transport expands the identity boundary. Before autonomous services connect, each delegation needs authenticated participants, a narrow grant, structured state, audit evidence, and a reliable way to revoke or deny the work.
Hypler technical analysis
Engineering notes
An agent-to-agent protocol creates an interservice control plane for capability discovery and task exchange. The message may describe work, but it cannot safely carry more authority than the caller is allowed to delegate. Each receiver therefore needs to authenticate the sender, evaluate the requested capability against local policy, and bind a returned task state to the original request. Interoperability increases the number of trust edges; it does not remove the need for local authorization and audit design.
What to inspect
- Participant identity
- Inspect the credential or identity assertion attached to a task request and how the receiving service validates its issuer and audience.
- Delegation record
- Inspect the requested capability, delegated scope, expiry, and correlation identifier that connects a subtask to its parent.
- Failure return
- Inspect behavior when a participant is unavailable, returns malformed state, or asks for an action beyond the caller's authority.
Scope and limits. Protocol-level collaboration does not establish shared trust, acceptable data handling, or authorization policy among connected services.
Terms and definitions
- AI Governance
- Policies, roles, controls, and review processes that guide how AI systems are selected, used, monitored, and retired.
- Evaluation
- A repeatable method for measuring a system against defined quality, safety, or task criteria.
- Model Provenance
- Documented origin and history of a model, including its publisher, version, artifacts, training claims, and modifications.
- Anthropic introduces the Model Context Protocol
Anthropic introduced the Model Context Protocol as an open protocol for connecting AI applications to external systems such as data sources, tools, and workflows.
- NIST releases AI Risk Management Framework 1.0
NIST released AI RMF 1.0 as a voluntary framework for managing risks in the design, development, deployment, and use of AI systems.
- NIST publishes the AI RMF Generative AI Profile
NIST AI 600-1 is voluntary guidance for applying the AI Risk Management Framework to generative AI through Govern, Map, Measure, and Manage.
Original source
Historical source briefing with Hypler engineering analysis. Source details reflect the original publication date; implementation examples are hypothetical. Technical analysis expanded October 24, 2026; this does not change the original source event or establish a new source verification. Editorial prose revised October 26, 2026; original event, publication and source-check dates are retained.