Anthropic adds remote MCP support to Claude Code
Anthropic announced remote Model Context Protocol support in Claude Code. The company said developers could connect Claude Code to remote MCP servers by adding a vendor URL instead of operating local servers.
By Hypler editorial team · Source: Anthropic.
Original source date: .
Hypler publication: . Hypler updated: .
Estimated reading time: 4 minutes.
Topics: Anthropic, MCP, Claude Code, OAuth

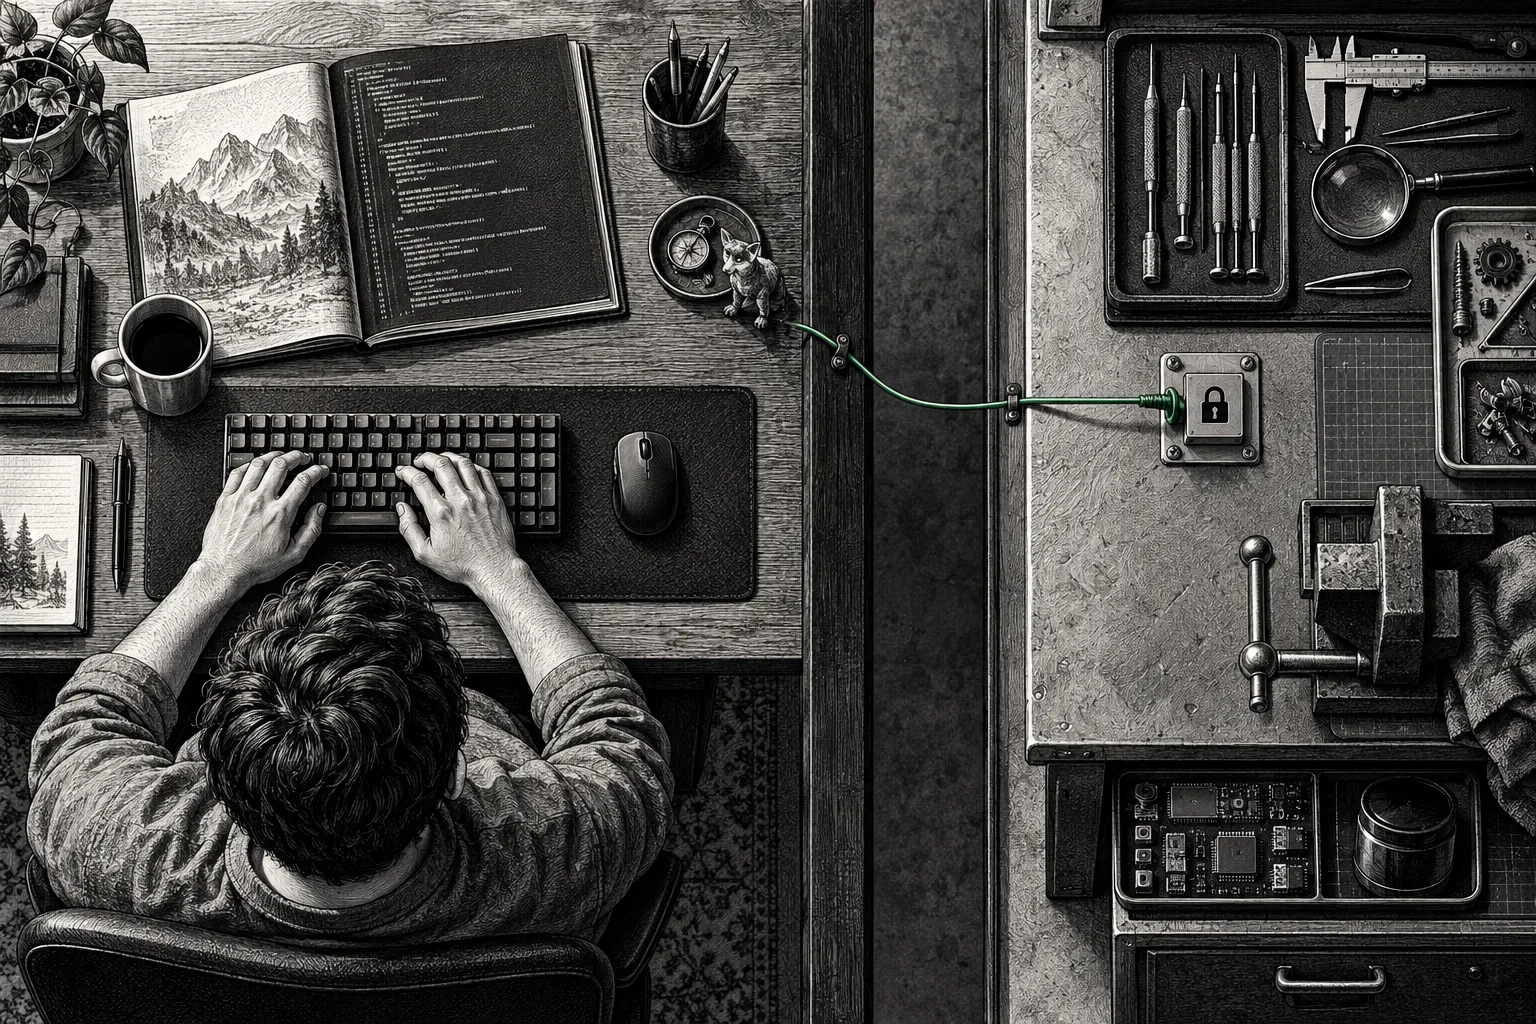
The remote server remains a separate service
Anthropic announced remote Model Context Protocol support in Claude Code on June 18, 2025. It said developers could add a vendor URL instead of operating a local server, then use exposed tools and resources. The announcement gave examples involving development tools, project-management systems, and knowledge bases, including Sentry and Linear, and described native OAuth. It placed updates, scaling, and availability with the remote-server vendor. The connection may remove local maintenance, but it introduces a service with its own identity model, capability catalog, change history, and failure behavior.
Treat the connection as a capability contract
MCP makes operations discoverable; it does not decide which should be permitted. Record each tool's input schema, output type, data classification, action effect, owner, and approval requirement. Read-only issue lookup carries different stakes from changing a ticket, editing a record, or publishing a release. OAuth establishes an authenticated connection, while the application still chooses scopes, session lifetime, revocation, and how a request maps to an identity. The endpoint, configuration version, approved scopes, and actual enabled tools should remain visible in an operational record, ready for review when the server changes.
Read-only issue context is a useful first boundary
Imagine a hypothetical code-review workflow that receives a pull-request identifier and can call one read-only issue-tracker tool. It fetches the linked issue title, acceptance checks, and approved labels, then includes those fields beside the source diff in a draft review. The output cites the issue identifier and revision. The connection has no tool for changing issue state or adding comments. An access error or repository mismatch becomes a recorded gap; a reviewer may correct the link or proceed with source-only review. The external system contributes context without becoming an excuse to expand access.
The endpoint is an input boundary, not policy
A remote server can alter its catalog, return incomplete resources, redirect a request, or go down. Returned text can contain imperative language that a model mistakes for trusted direction. Treat it as data, validate tool arguments against schemas, and apply action policy after a response as well as before it. Test expired authorization, revoked access, added tools, changed schemas, malformed responses, delays, and a resource asking the agent to do unrelated work. The desired result is a clear error category tied to the original task, with state-changing work still pending review.
Integration evidence should outlast setup speed
Build fixtures for expected resources and responses, including permission failures and changed fields. Confirm that the agent calls only allowed operations, makes use of returned information traceable, and remains in scope when the external system fails. Review OAuth scopes, account ownership, logs, and revocation with the connected service's owners. A rollout can start with a read-only server in a limited workspace and telemetry for connection failures and tool calls. Consequential tools need separate tests for receiving-system behavior, authorization, retries, and receipts before they are enabled.
Convenience does not reduce accountability
A vendor URL may spare the team from hosting a local server; it cannot spare the team from knowing who may use which remote effect. Hypler's analysis treats remote MCP as a reviewed software dependency with bounded capabilities and accountable ownership. The historical announcement does not establish that a specific server is available, safe, or authorized for a specific task. Revisit the connection when its catalog, OAuth configuration, or workflow changes. That is where the actual reliability and security question resides.
Hypler analysis
Hypler’s view
Remote context is remote capability. Adding a URL can add identities, scopes, data paths, and side effects to an agent, so each server connection deserves a dependency review rather than a convenience exception.
Hypler technical analysis
Engineering notes
Remote MCP moves tool discovery and operation from a local process into a networked provider boundary. A vendor URL and OAuth connection therefore become part of the system's authorization graph: client identity, granted scope, exposed operations, returned data, and action evidence require independent inspection.
What to inspect
- Server capability inventory
- List every exposed tool and resource, its input schema, effect type, data domain, and whether it can read, write, or trigger an external action.
- OAuth grant
- Inspect client identity, consented scopes, token storage path, renewal behavior, revocation path, and the resource account represented by the connection.
- Call evidence
- Trace a denied request, a changed server response, and a retried action; inspect logs for selected operation, supplied arguments, authorization decision, and resulting outcome.
Scope and limits. Remote support lowers local server operation. It does not verify vendor service behavior, make a tool appropriate for a task, or establish permission to use connected data.
Terms and definitions
- MCP
- Model Context Protocol, an open protocol for connecting AI applications to tools, data sources, and prompts through defined interfaces.
- Tool Calling
- A model interface pattern where the model requests a structured operation from an external tool.
- API Layer
- The server-side interface that exposes defined data and actions to clients or integrations.
- Testing and Observability
- Testing checks expected behavior; observability uses runtime signals to understand a system’s actual behavior and condition.
- Anthropic adds code execution, MCP connector, Files API, and caching
Anthropic announced four API capabilities for agents: a code-execution tool, an MCP connector, a Files API, and extended prompt caching.
- Docker adds agent-focused building blocks to Compose
Docker announced agent-focused building blocks for Docker Compose, describing a compose.yaml-based way to define models, agents, and MCP-compatible tools together.
- Docker announces an MCP Catalog and Toolkit
Docker announced the Docker MCP Catalog and MCP Toolkit for discovering, launching, and managing Model Context Protocol servers.
Original source
Historical source briefing with Hypler engineering analysis. Source details reflect the original publication date; implementation examples are hypothetical. Technical analysis expanded October 24, 2026; this does not change the original source event or establish a new source verification. Editorial prose revised October 26, 2026; original event, publication and source-check dates are retained.